The US tightens curbs on China’s remote access to AI chips as Europe faces mass hoax bomb threats and regulators warn of rising nuclear risk in Ukraine.
Why Washington Is Tightening China’s Access to AI Chips
The US China AI chip war has mostly been described as a fight over physical hardware: which graphics processors (GPUs) Nvidia and others may ship to China. The latest move targets something less tangible, computing power rented over the internet.
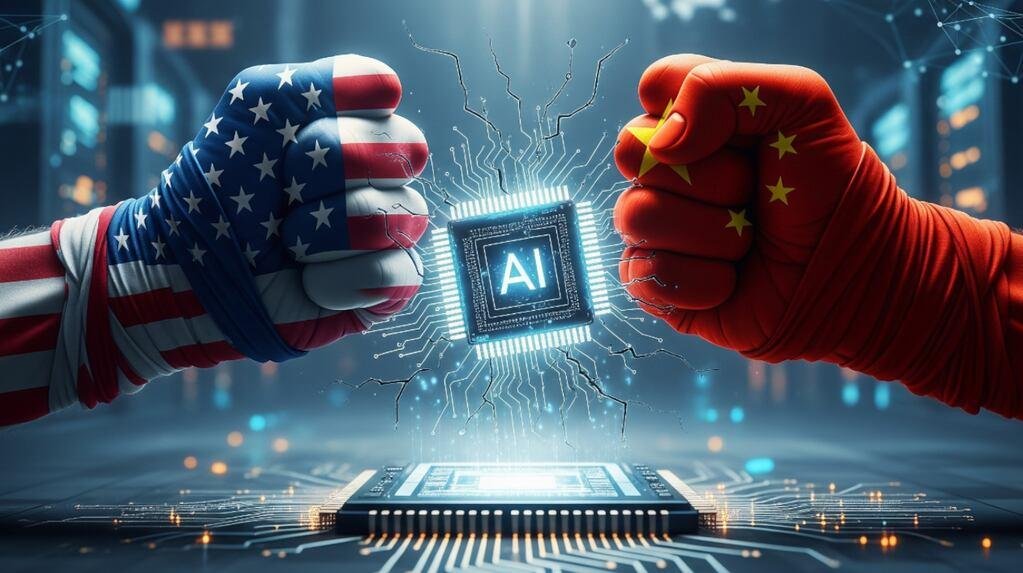
Under existing controls, Chinese companies cannot import the most advanced chips. But they could, until now, legally use top-tier computing capacity housed in data centres in third countries, particularly in Southeast Asia, according to Al Jazeera’s reporting on the rule. The Commerce Department’s Bureau of Industry and Security (BIS) has now issued an interim final rule, titled “Addressing Remote Access to Advanced Semiconductors” in the text China’s foreign ministry addressed on Tuesday.
As Bloomberg and The Japan Times describe it, data-centre operators in those five countries will need a US licence before exporting advanced AI chips from Nvidia and other American makers to customers there. Facilities already serving China-headquartered companies with significant volumes of computing power have 90 days to obtain licences, Reuters reported via The Globe and Mail. The same report says the rule formally rescinds a Biden-era regime that limited global access to AI chips through licensing. Business Standard reports the rules take effect November 19. Some uses, such as data centres running commercial recommendation systems for retailers or social platforms, are exempt, according to Bloomberg’s syndicated report.
The US national security argument is straightforward. Commerce says the rule exists so that restrictions on sensitive American technology “cannot be circumvented” through remote arrangements. If advanced chips are off-limits to Chinese buyers but their output is available by the hour from a server rack in another country, the control has little practical meaning. The Institute for Progress, a US think tank, estimates remote access could account for a quarter of China’s AI computing capacity by the end of 2026, per Business Standard’s summary.
There is also a domestic political story. Reuters reported that the department had been criticised over whether it was doing enough, and that enforcement delay let billions of dollars’ worth of restricted Nvidia chips reach data centres serving Chinese AI firms. The rule follows the November 12 resignation of Nvidia chief executive Jensen Huang after reports of extramarital affairs, one with a Megaspeed executive. Megaspeed is a Singapore-based cloud company under scrutiny over alleged chip diversion. Unnamed US officials have alleged she was recruited by China’s Ministry of State Security; Beijing calls that groundless. These are allegations, not proven facts, and I found no public charges in the sources reviewed. Colette Kress is serving as interim CEO.
How China’s AI Industry Could Be Affected
At a Tuesday briefing, foreign ministry spokesperson Guo Jiakun called the rule a “typical act of economic coercion and long-arm jurisdiction”. The Chinese foreign ministry’s official transcript is the primary source. The Next Web notes the timing: days before a planned Trump–Xi meeting at APEC in Shenzhen, with a minerals-deal deadline also looming.
Practically, the squeeze falls on Chinese AI developers who trained or served models on rented overseas capacity. They face three options: pay more for licensed access that may not be granted, shift workloads to Chinese-made chips that are generally regarded as less capable, or look for gaps elsewhere. CNBC reported that a Chinese lab, Moonshot AI, sought Nvidia capacity through European data centres, a sign that the search for workarounds is already global. CNBC also reports Nvidia told customers it will not sell to buyers who rent more than half their GPUs to Chinese companies, and that Congress is considering a Remote Access Security Act that would give Washington broader authority.
The global effects reach beyond China. Operators and exporters must now examine who owns and controls their customers, which raises compliance costs across the global semiconductor supply chain. Singapore said it is studying the measure carefully, and Bloomberg noted the rule risks irritating regional partners as well as Beijing. For the US, the strategic bet is that denying compute slows rivals more than it accelerates their self-reliance. Critics of export controls have long argued the opposite, and the evidence remains contested.
Europe’s Hoax Bomb Threats and the Growing Security Challenge
The disruption has come in waves. According to Reuters’ investigation, syndicated by Internazionale, threatening emails first reached schools in Northern Ireland and Scotland on October 19. i24NEWS says Hungary and Serbia were also hit. More than 50 flights across Europe were targeted between November 2 and 6, and Irish broadcaster RTÉ evacuated staff on November 6.
The largest day was November 11. About 6,300 Italian schools received a warning of an explosive device with a remote trigger, and more than 300 were evacuated, per Reuters’ coverage. Police said roughly 1,000 schools in Scotland and 300 in Northern Ireland got the same message, and Irish media reported about 300 more in the Republic. CNN reports a further 3,778 Italian schools were targeted the next day and that Rome issued a new response protocol.
What do investigators actually know? Police in Scotland said inquiries found no credible threat, and the threats have all proven false. Security firm Mimecast found the November campaign hit almost the same Scottish schools as October, suggesting a shared target list. Some messages carried the branding “Misogynistan” or “Male State”, which tells us what the sender wanted people to see, not who the sender is.
What remains unconfirmed is attribution. French interior minister Laurent Nuñez said he sees “a possibility of foreign interference, very clearly”, naming Russia and “other countries, potentially”. Police Scotland says it cannot rule out a link between waves. Russia and Iran have denied involvement, and Reuters could not independently establish that one group sent every email. Ukrainian officials have previously accused a suspected Russian mercenary hacker group of using bomb hoaxes, but that is background, not evidence for this campaign. Europol is trying to trace the source.
The challenge for European security is asymmetry. An email costs almost nothing; each one forces a decision. Head teacher Chris Donnelly in Belfast told Reuters he doubted the message but still searched room by room, because treating a threat casually is the one error that cannot be undone. Multiply that by thousands of institutions and you get lost teaching time, strained police resources and eroded public confidence. That is the point of such a campaign, whoever runs it.
Why Ukraine’s Electricity Infrastructure Raises Nuclear Safety Concerns
Nuclear plants do not just produce electricity; they consume it. Even a shut-down reactor keeps generating heat that must be removed by pumps and cooling systems, which need reliable power from the external grid. If that fails, plants fall back on emergency diesel generators, which are designed as a last line of defence, not as routine supply.
That is why the International Atomic Energy Agency has been blunt. In Update 375 on November 14, Director General Rafael Grossi said grid instability from military activity forced power reductions at several operating Ukrainian units. At the Russian-occupied Zaporizhzhia plant, all off-site power was lost for more than 12 hours on November 8 after damage to a 330 kV line. The Kyiv Independent counts it as the plant’s 27th complete off-site power loss since the invasion, and The Moscow Times reports the plant has relied on a single line since late March. Russia and Ukraine blame each other for the line damage.
Update 374 on November 6 said strikes on substations caused several plants to lose off-site lines, and that IAEA teams logged 123 air-raid alerts at four sites in a week. Newsweek reports backup generators started at facilities in the Chernobyl exclusion zone after grid dips.
On November 16, regulators from 38 countries urged Russia to stop attacking nuclear facilities and the energy infrastructure they rely on, as reported by Reuters via ZeroHedge’s copy of the joint statement and the Moscow Times. One official described a nationwide blackout hitting all of Ukraine’s operating reactors at once as the worst case.
Chernobyl matters here as context, not as a forecast. The 1986 disaster was caused by a flawed reactor design and a botched safety test, not a grid failure, and Ukraine’s current reactors are of a different type. The closer technical lesson comes from Fukushima in 2011, where lost power meant lost cooling. The honest reading of today’s warnings is that safety margins are thinning each time a line is cut, and winter demand makes recovery harder. IAEA and regulators say the risk can be prevented if the attacks stop.
What These Three Developments Reveal About Global Security
On the surface, a chip rule, a hoax email and a transmission line have little in common. Underneath, each shows how global security risks now run through shared systems: cloud computing, email and inboxes, and the electricity grid.
In each case the weapon or the weakness is access. Export controls now govern who can rent compute, not only who can buy chips. A single email can be sent to thousands of schools at once. A damaged substation can become a nuclear safety question. Defence, in turn, becomes a matter of coordination among agencies, companies and allies rather than any one ministry.
Evidence standards differ too. The chip rule is documented policy; the Nvidia-related espionage claims are unproven allegations; the hoax attribution is suspicion; and the nuclear warnings are expert risk assessments from the IAEA and regulators, not predictions of an accident.
What the US and UK Should Watch Next
For the US: Watch the licensing process. Whether Commerce grants licences, how fast, and how Nvidia’s leadership transition affects its stance on China will determine whether the rule bites. Also watch Congress’s Remote Access Security Act and whether Beijing’s promised measures touch US firms or critical minerals ahead of the Trump–Xi meeting.
For the UK: Scotland and Northern Ireland were directly targeted, and Police Scotland’s cyber and fraud unit is working with UK and overseas agencies. The questions are whether Europol or national agencies produce an attribution, and whether schools and emergency services need clearer protocols to tell a hoax from a credible threat quickly. On energy and nuclear safety, I could not find a UK government statement specific to these Ukrainian warnings, so none is attributed here.
For both: Look for updated IAEA statements as winter deepens, any grid repairs at Zaporizhzhia, and whether allies supply the transformers and cables Ukrainian officials say they need.
Conclusion
These stories should not be fused into one narrative of coordinated menace. The evidence does not support that, and no source reviewed claims it. What they do show is a world where the infrastructure of daily life, from computing capacity to school email accounts to power lines, has become contested ground. The sober response is neither alarm nor complacency. It is precise attribution, enforceable rules and resilient systems, and keeping fact, allegation and forecast clearly apart while the facts keep changing.
Frequently Asked Questions
Why is the US restricting China’s access to AI chips? The US government argues advanced AI hardware has national security uses and that China should not obtain it by any route. The new rule targets remote access through overseas data centres because Chinese firms could rent capacity they were barred from importing.
How will AI chip restrictions affect China? Chinese developers may face higher costs, licensing hurdles or reliance on less capable domestic chips. The size of the impact depends on how licences are granted and how quickly workarounds emerge.
Why are European schools receiving hoax bomb threats? The motive is unconfirmed. The emails appear designed to cause disruption and fear, and officials suspect foreign interference, but no group has been publicly identified and Russia and Iran deny involvement.
Could attacks on Ukraine’s power grid cause a nuclear accident? The IAEA and 38 national regulators warn that repeated loss of external power erodes safety margins, but plants have backup systems and regulators say the risk is preventable if attacks on energy infrastructure stop.
What do recent security threats mean for Europe and the United States? They point to growing vulnerability in shared infrastructure, from cloud computing to email and electricity. Responses depend on coordination among governments, companies and allies.
Sources and Further Reading
- Al Jazeera: US moves to block China’s remote access to AI chips
- Bloomberg: US moves to curb China’s remote access to Nvidia’s AI chips
- CNBC: Nvidia warns chip buyers of legal risks
- China’s Foreign Ministry press conference, November 17, 2026
- Reuters (syndicated): ‘Death is near’ hoax bomb threats
- CNN: Europe scrambles to respond to wave of bomb threats
- IAEA Update 375
- IAEA Update 374
- Kyiv Independent: Regulators warn of rising nuclear accident risk